Artificial intelligence is transforming the way businesses operate. From streamlining daily processes to improving productivity and decision-making, AI is creating opportunities that were difficult to imagine just a few years ago.
Unfortunately, cybercriminals are discovering those same opportunities.
AI is changing the cybersecurity landscape, giving attackers new ways to create convincing phishing messages, impersonate executives, manipulate digital communications, and automate aspects of their attacks. What once required significant technical expertise can now be accomplished more quickly, at greater scale, and with fewer resources.
For businesses, this means traditional approaches to cybersecurity may no longer be enough.
The New Face of Cybercrime
Cyberattacks are not necessarily becoming more complicated. They are becoming more convincing.
Generative AI allows cybercriminals to produce highly personalized emails, replicate writing styles, translate communications, and create realistic audio and video impersonations. These capabilities make it increasingly difficult for employees to distinguish legitimate business communications from fraudulent requests.
Consider a few scenarios:
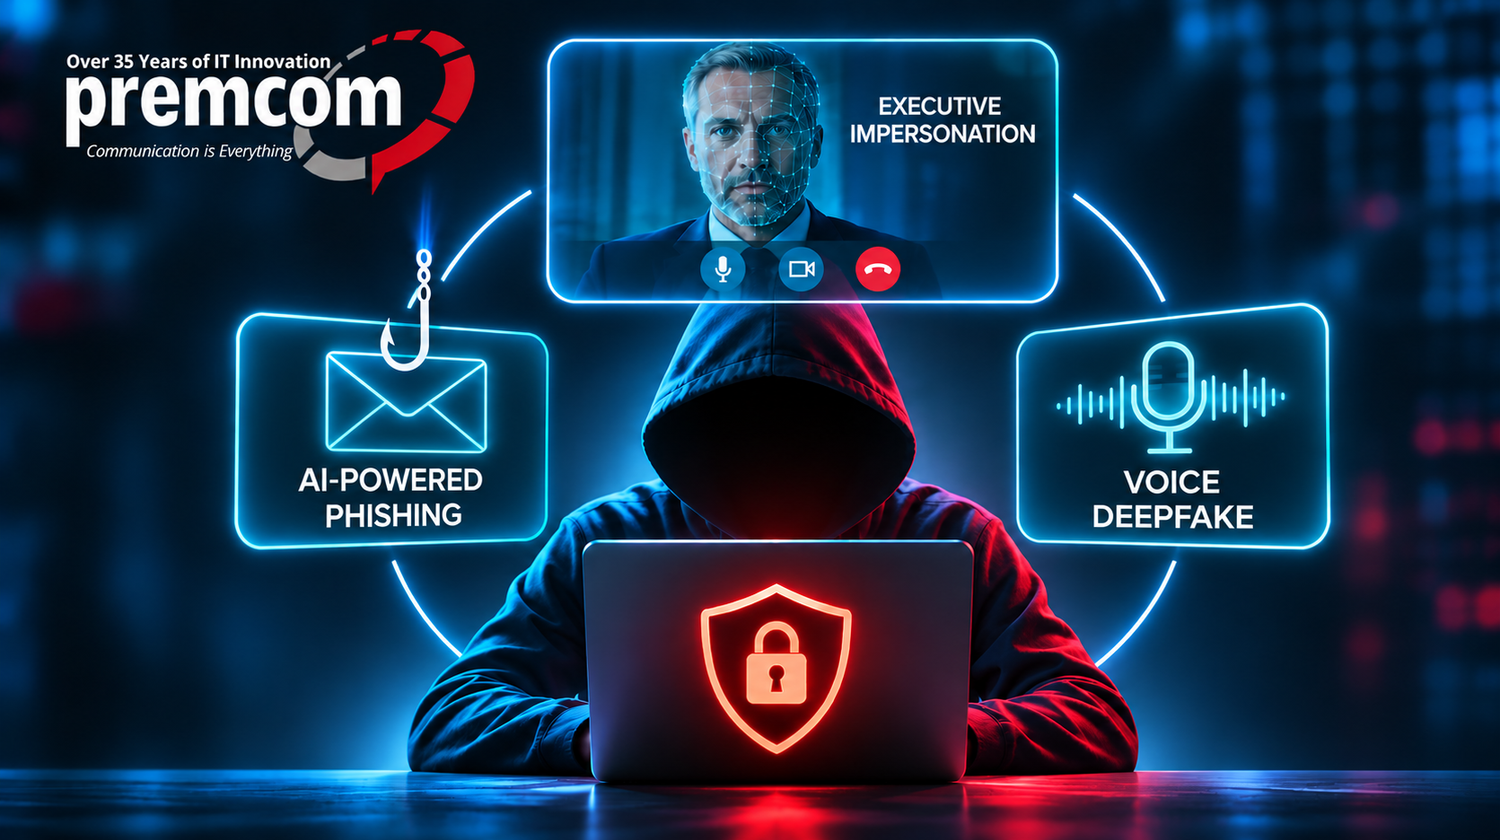
AI-Powered Phishing: Employees receive emails that appear professionally written, reference legitimate business activities, and are personalized to their roles. The grammatical errors and awkward wording that once helped identify suspicious messages may be absent.
Executive Impersonation and Deepfakes: Criminals use AI-generated voices or video to impersonate company executives, vendors, or other trusted individuals. An employee may receive what appears to be an urgent request from a company leader to transfer funds or share sensitive information.
Business Email Compromise: Attackers use publicly available information and compromised accounts to create convincing conversations with employees, customers, or vendors. AI can help personalize messages and make fraudulent communications more credible.
Automated Reconnaissance: AI tools can help attackers gather and analyze publicly available information about an organization, its employees, and its technology environment, helping them develop more targeted approaches.
The danger is not simply that these attacks look more sophisticated. It is that they exploit something every business depends on: trust.
What the Latest Research Tells Us
The growing concern surrounding AI-driven attacks is supported by recent industry research.
In September 2026, Gartner published its analysis, How AI Is Changing the Cyberthreat Landscape, highlighting how artificial intelligence is increasing the speed, reach, and sophistication of social engineering attacks.
One particularly concerning finding: 41% of surveyed organizations reported at least one social engineering incident involving a deepfake during an employee audio call in the previous 12 months.
Gartner also found that 79% of surveyed CISOs reported at least one email phishing, spear-phishing, or business email compromise incident during that period.
These findings reinforce an important point: AI-powered deception is not simply a future possibility. Organizations are already encountering these threats.
Gartner emphasizes that businesses need to move beyond relying on employees to visually identify fake communications. Instead, organizations must establish stronger verification procedures, protect employee identities, and improve their ability to detect and respond to suspicious activity.
Five Ways Businesses Can Strengthen Their Defenses
While no cybersecurity strategy can eliminate every threat, organizations can take meaningful steps to reduce their exposure and limit the potential impact of an attack.
1. Strengthen Employee Security Awareness
Employees remain an important line of defense. Regular security awareness training should address evolving threats, including AI-generated phishing, executive impersonation, fraudulent vendor requests, and deepfake communications.
Most importantly, employees should understand that convincing emails, familiar voices, and realistic video calls are not proof of someone's identity.
2. Establish Verification Procedures for Sensitive Requests
Create clear procedures for verifying requests involving financial transactions, changes to vendor payment information, password resets, and access to confidential information.
Use a separate, trusted communication channel to verify unusual or urgent requests. For example, if an employee receives a request to change a vendor's banking information, they should independently contact the vendor using a previously verified phone number.
High-risk financial transactions should also require appropriate approval from more than one authorized individual.
3. Strengthen Identity and Access Security
Stolen credentials remain a significant avenue for attackers.
Businesses should implement multifactor authentication, prioritize phishing-resistant authentication where practical, enforce strong access controls, and limit user permissions to what employees actually need.
Privileged accounts deserve particular attention because unauthorized access can create significant opportunities for attackers.
4. Implement Proactive Threat Monitoring
Traditional security measures alone may not provide sufficient visibility into today's evolving threats.
Businesses should consider layered security solutions that provide continuous monitoring of endpoints, networks, user activity, and suspicious account behavior.
Identifying unusual activity early can help organizations investigate potential compromises and respond before an incident escalates.
5. Develop and Test an Incident Response Plan
Every organization should know what to do when a suspected cyberattack occurs.
Establish clear reporting procedures, identify who is responsible for responding, and ensure employees know how to escalate suspicious communications.
Incident response planning should include scenarios involving compromised email accounts, fraudulent financial requests, stolen credentials, and suspected executive impersonation.
A plan that has never been tested may not be effective when a real incident occurs.
AI Can Strengthen Cybersecurity, Too
It is important to recognize that artificial intelligence is not exclusively a tool for cybercriminals.
Security professionals are also using AI to improve threat detection, analyze suspicious activity, identify vulnerabilities, prioritize security alerts, and accelerate incident response.
The challenge for businesses is ensuring that their security strategy evolves alongside the technology.
AI adoption should be accompanied by appropriate governance, data protection, access controls, and security oversight. Organizations also need to understand how employees are using AI tools and whether confidential company information is being exposed through unapproved applications.
The objective should not be to avoid AI. It should be to adopt it responsibly while preparing for the security challenges that come with it.
The Bottom Line: Cybersecurity Must Keep Evolving
Artificial intelligence is changing the way businesses work, but it is also changing the way businesses are targeted.
Organizations can no longer rely solely on traditional email filters, firewalls, or annual security awareness training. A stronger approach requires multiple layers of protection, continuous visibility, employee education, and a proactive cybersecurity strategy.
For business leaders, cybersecurity is not simply an IT concern. It is a business risk that can affect financial stability, customer relationships, operational continuity, and organizational reputation.
At PremCom, we believe protecting your business starts with understanding the risks, strengthening your technology infrastructure, and taking a proactive approach to security.
Don't wait for a breach to discover where your vulnerabilities are.
Learn how PremCom can help your organization strengthen its security posture and prepare for an evolving threat landscape.
PremCom — Stronger IT infrastructure. Smarter security.
Visit www.premcom.com to learn more.